THE PLATFORM
Your compliance program, pre-structured and ready to run.
domainGRC replaces the “spreadsheets and shared drives” approach with a connected compliance system, loaded with your framework controls, your compliance calendar, and the expert practitioner-built policies your auditor expects to see.
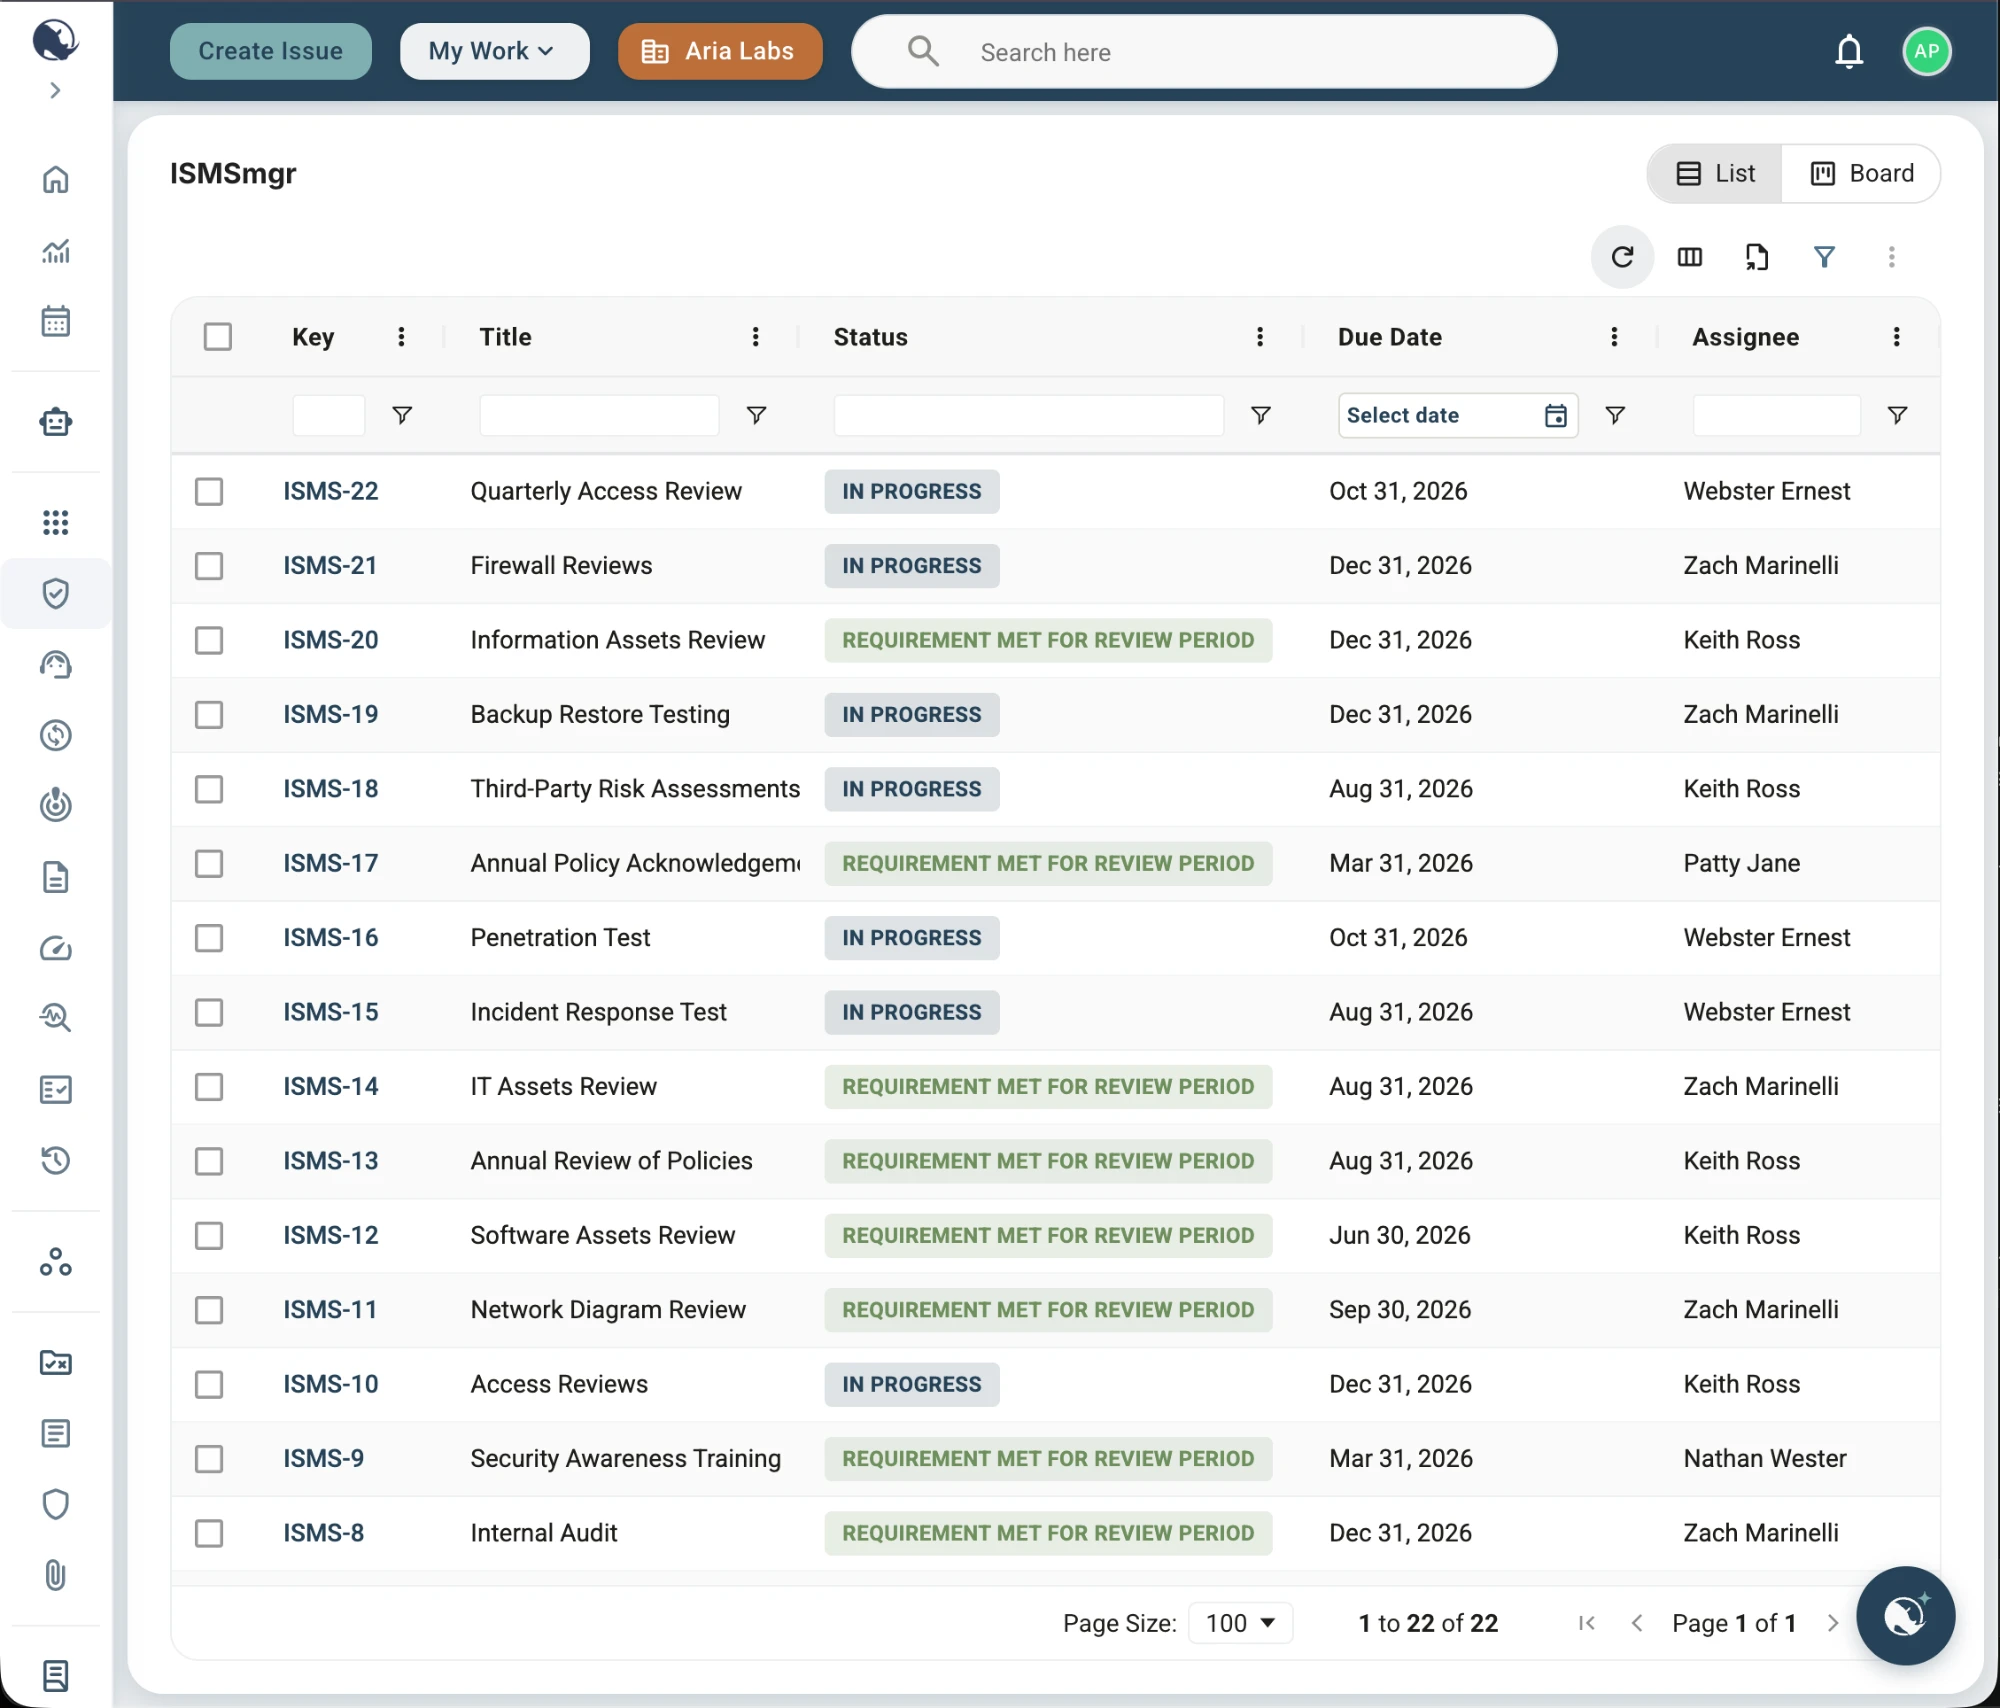
How the platform is organized.
domainGRC is organized around three areas that mirror how a real compliance program operates: managing your ongoing compliance activities, tracking the assets your program covers, and running your audit when the time comes. Everything connects.
myDomain: Run your compliance program
The operational core of your compliance program. This is where your recurring activities live, your IT service desk runs, your risks are tracked, and your corrective actions are managed.
- Pre-loaded with framework controls
- Compliance calendar on day one to help you hit the ground running
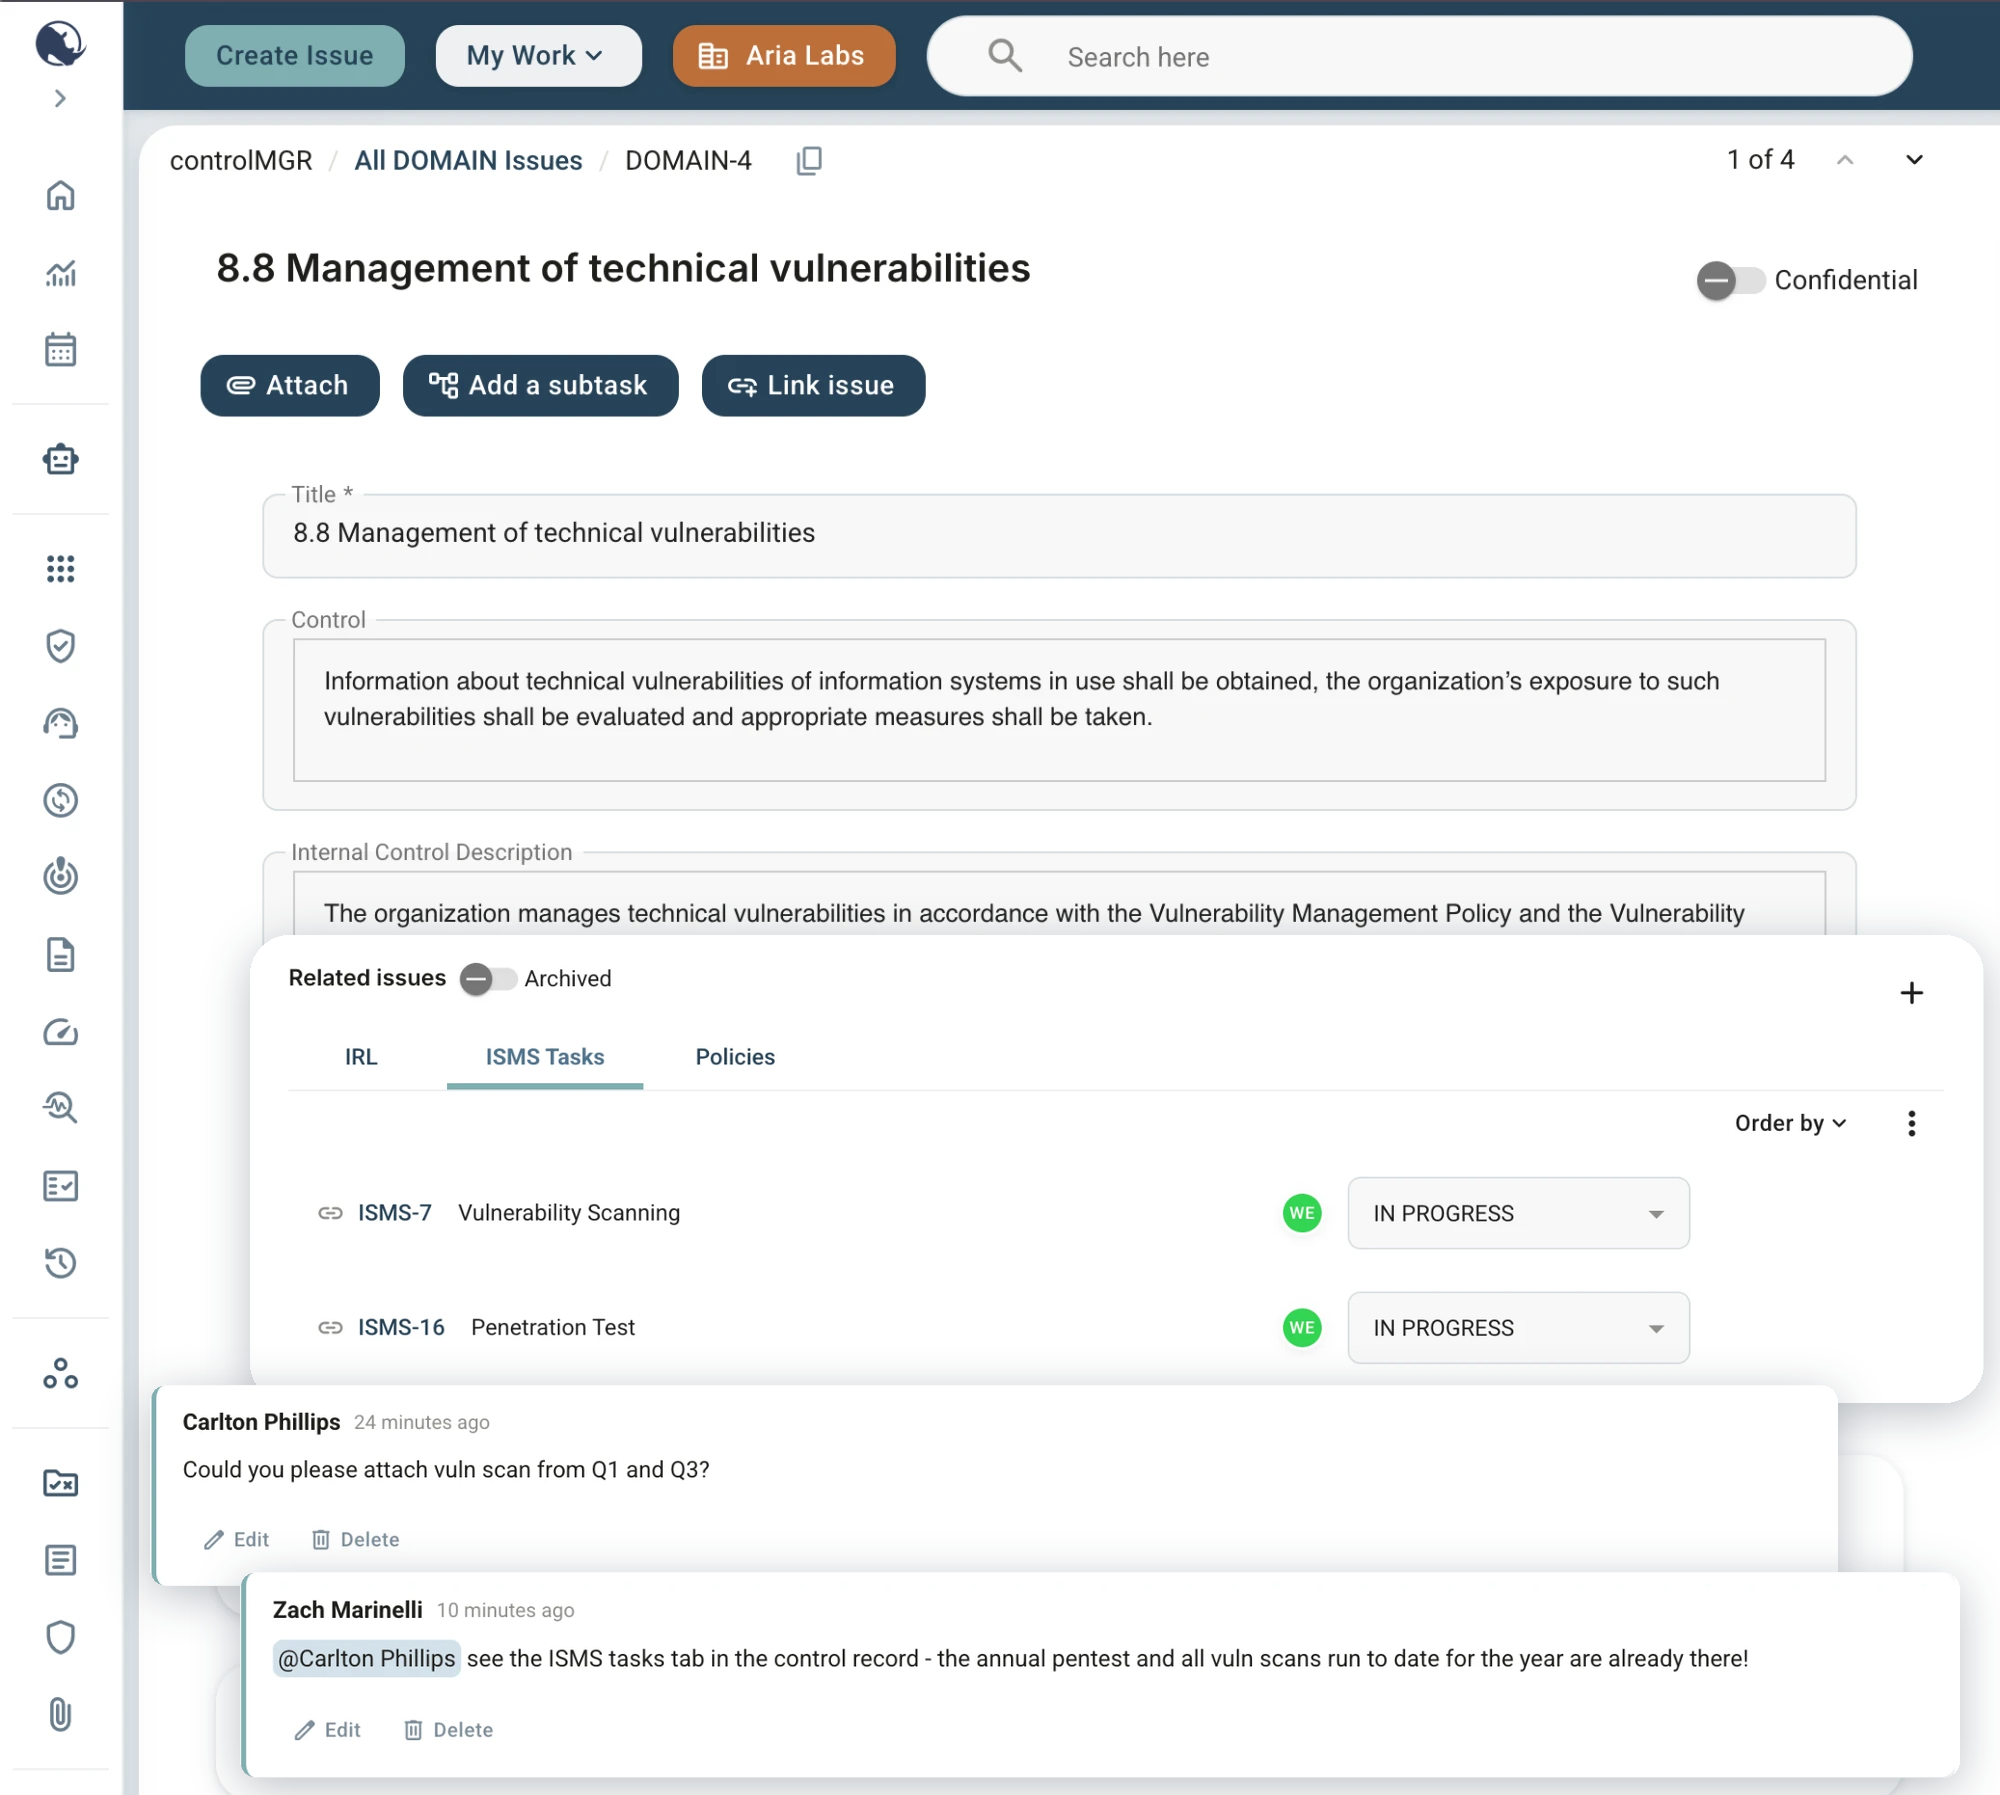
- Evidence flows to every control it supports - no repeat uploads
assetMGR: Know what you’re protecting
A structured inventory of all organizational assets.
- Link any asset to the controls and risks that govern it
- Understand related assets that shape the risk profile
- Audit trails of employee lifecycle events, access requests, hardware provisioned, and maintenance performed.
myAudit: Where you and your assessor work together
Upload your assessor’s Information Request List to domainGRC and invite them directly into your domain with scoped, time-limited access.
- Assessors review and approve evidence or request additional info live
- Artifact owners notified automatically when items need rework
- Track audit status through theDash in real-time
Interconnected web
Every record can be linked to every other - people, software, hardware, information, and facilities are stored as an interconnected web.
- Understands the ripple effects when anything changes
AI compliance assistant
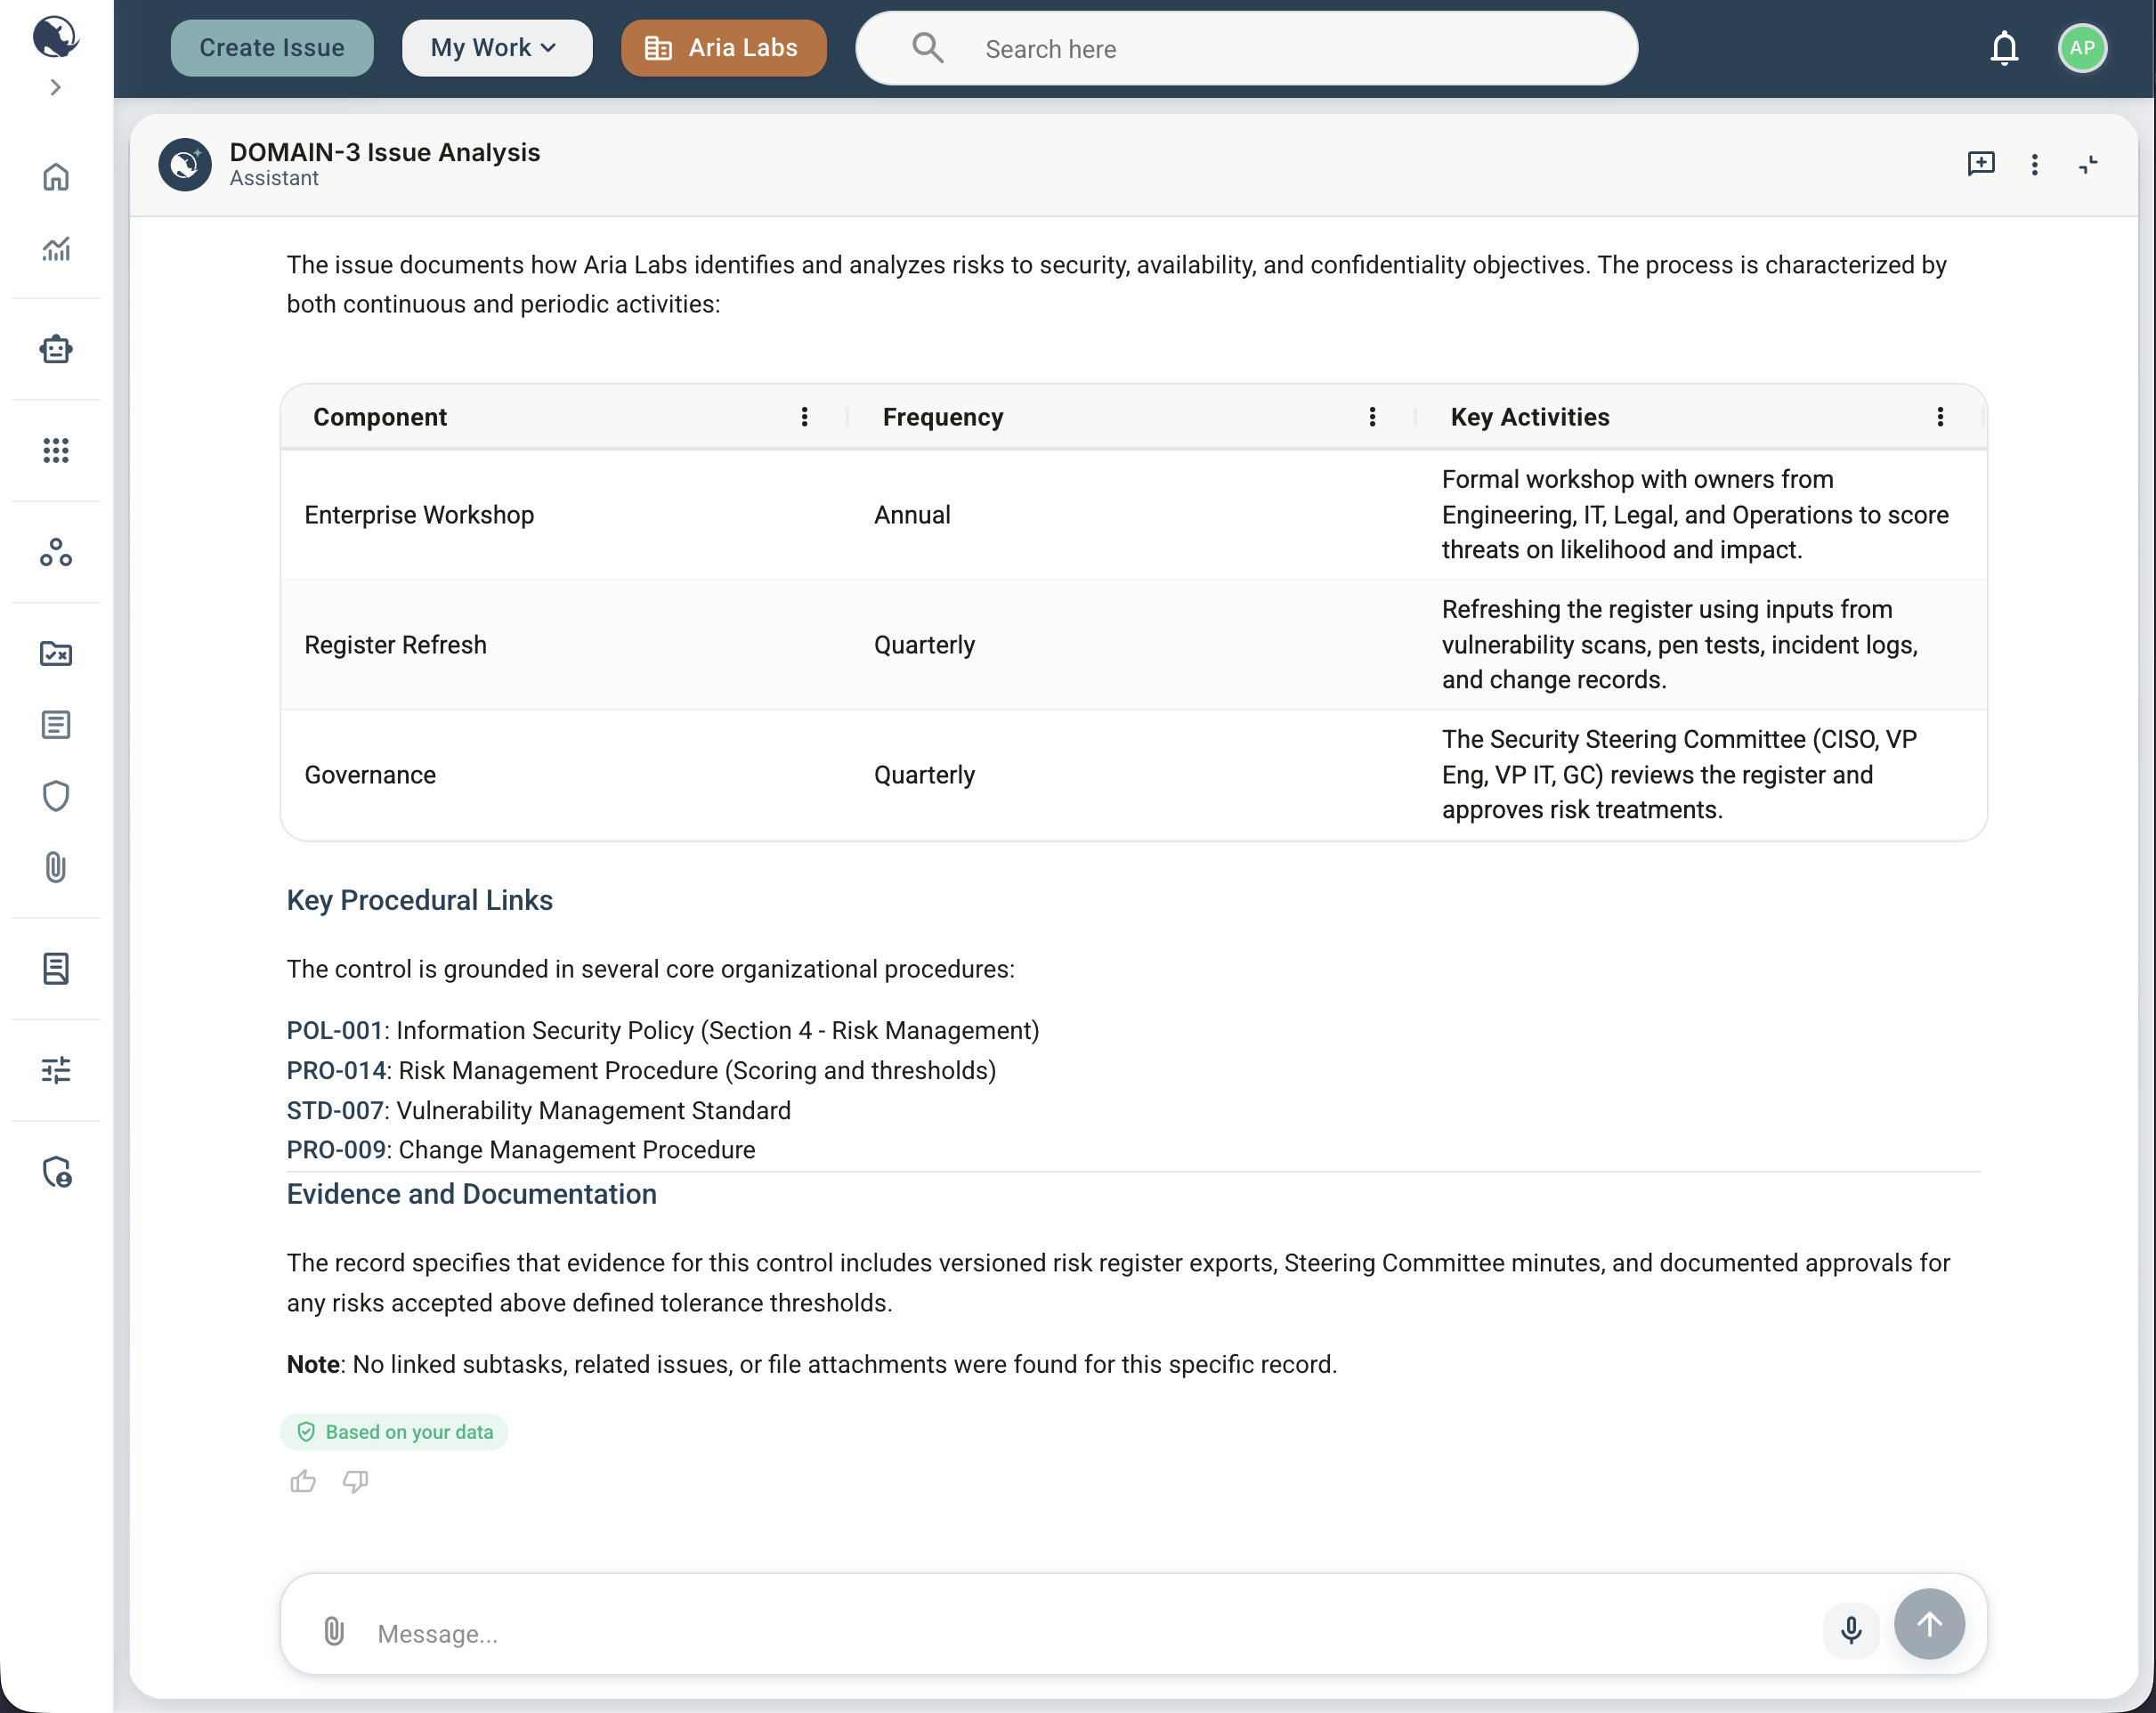
A conversational AI assistant helps you get answers faster. Ask questions about your program, generate compliance documents like a Business Impact Analysis, or explore how risks and controls connect across your environment - all in a natural language.
Audit trail with field-level change history
Every change to every control, asset, and artifact record is timestamped and attributed to a specific user.
- Always know who changed what, and when it happened
Evidence library with versioning
Centralized evidence and controls that travel across audit periods as things change.
- Historical context from your last audit is archived but remains available for reference
Assessor collaboration in-platform
Give assessors scoped, time-limited access to review evidence live and work through your Information Request List directly in the platform.
- Assessors flag items needing rework, notifying artifact owners automatically
Multi-framework support, no upcharge
All your frameworks in one place. The platform grows with you as you need new frameworks or expand scope.
- No upcharges for adding additional frameworks
This year's work becomes next year's blueprint.
domainGRC replaces spreadsheets with a structured rollover system. After each audit, the platform retains:
- Tested controls and collected evidence
- Cited policies and assessed risks
- Owners who closed each task
Next year’s cycle starts from last year’s blueprint. Recurring controls roll over with one click. Anything that changed since the last cycle (new assets, new vendors, new policies, departed owners, expanded scope) is flagged for review. Each cycle becomes more efficient than the last, because you are refreshing a working record instead of rebuilding a spreadsheet.
MOBILE APPS
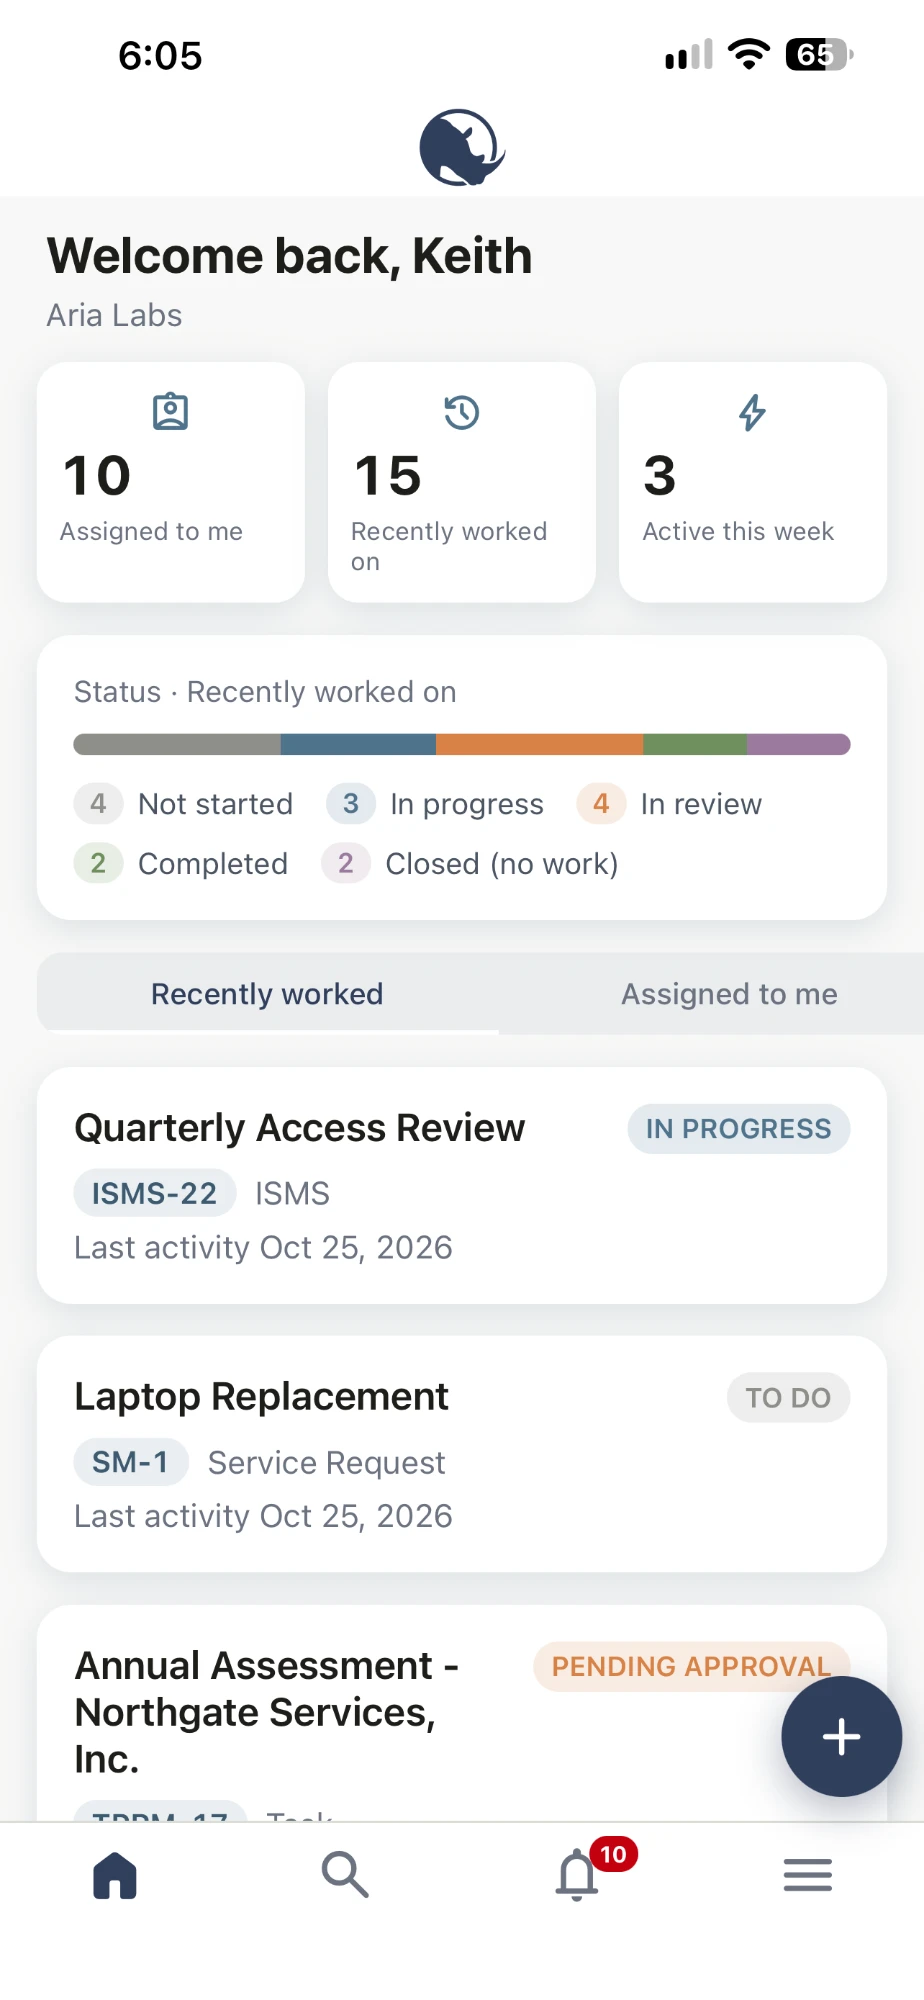
Compliance work does not wait for a desk.
domainGRC ships native applications for iOS and Android. Authorized users sign in to the same domain, see the same records, and work under the same permissions as they do on the web.
- Browse, edit, and file issues of any type, from service requests to security incidents
- Run safety inspections from your phone, with photos attached to each finding
- File incident reports on the spot, routed straight into corrective actions
- See and complete scheduled maintenance for the assets in front of you
- Offline-first: anything captured without a signal is queued and syncs when you reconnect
- Push notifications when a record needs your attention
Nothing new to administer — your organization creates every account. The app is just another door into the program you already run.
AI-NATIVE COMPLIANCE PLATFORM
Built for AI from the data up.
Our AI compliance assistant works inside your program. Each session is bound to a single organization, and that scope is enforced server-side. Before it answers, the assistant queries your data.
- Searches your issues, audits, and attachments, including the text inside uploaded PDFs and SOPs
- Answers questions only from documents in your knowledge base, and cites the source file behind every answer
- Reads the exact figures from your live program data to answer questions and build charts
- Creates and updates records, from issues to audits after echoing the plan back to you for confirmation
What you can do on day one.
One system, one set of records, and an internal audit capability for reviewing your program before your assessor does.
- See the whole program at a glance: audit status, upcoming activities, overdue tasks, risk distribution, and corrective action progress in one configurable dashboard.
- Work every framework control as a structured record. All frameworks get imported at onboarding.
- Keep a structured risk register: log every known threat, assign a rating, link it to corrective actions, and track remediation to closure.
- Manage corrective and preventive actions in one place, each linked to the risks, controls, and assets it touches.
- Run the policy lifecycle and reference the current version of every policy, standard, and procedure your program needs.
- Hold a complete compliance inventory: users, vendors, licenses, laptops, network equipment, cloud infrastructure, products and services you sell, the information processed or stored across your organizational assets - along with all metadata.
- Document vendor profiles, link them to the software and data they access, and let the platform automate annual risk assessments - send each vendor a personalized URL to complete forms and upload documentation directly.
- Run onboarding, offboarding, and access requests through a built-in service desk, so the evidence for those controls captures itself in the normal course of work.
- Record changes and security incidents where the rest of the program lives, not siloed in a disconnected tool.
- Load your assessor’s Information Request List, assign evidence, and track each item through to acceptance.
- Upload every artifact once and reuse across frameworks.
- Build the report you need in seconds: filter, sort, group, and configure any view, then save, share it, export it or build it into your dashboard.
Every framework your program requires. No per-framework fees.
Build your domain with all the framework controls for the certifications your business needs. Overlapping controls are mapped so you can capture evidence once and reuse it across multiple controls and frameworks. The platform is designed to be extensible. If the framework can be audited, domainGRC can support it.
Risk management, corrective actions, third-party risk management, and internal audit capabilities are included in every plan. We don’t gatekeep the features you actually need to pass a real audit. And we don’t believe in nickel-and-diming you for streamlining your compliance program.